SMTP Brute-Force Protection
Protection overview
RdpGuard protects your SMTP server from brute-force attacks.
It monitors mail server logs or unencrypted SMTP traffic and blocks the attacker's IP address when the number of failed login attempts reaches the configured limit.
Enable and configure SMTP brute-force protection
Open RdpGuard Dashboard and click SMTP under Monitored protocols.
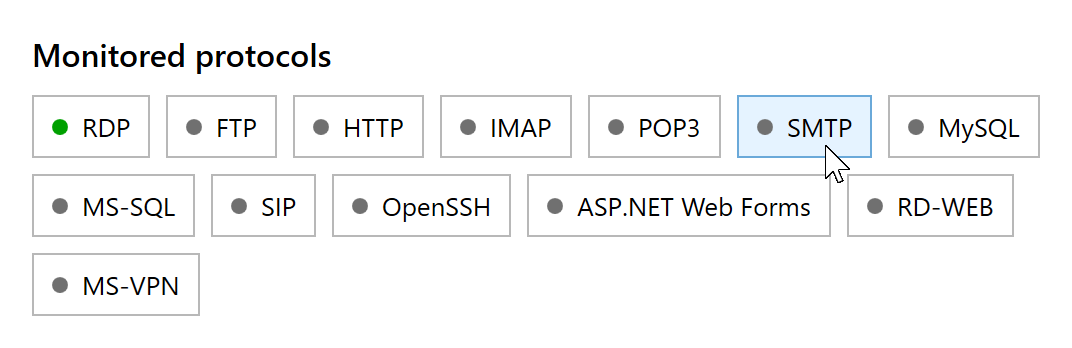
Click SMTP to open its protection settings. Select Enable SMTP protection, choose a monitoring method and configure it as described below. Then click Save.
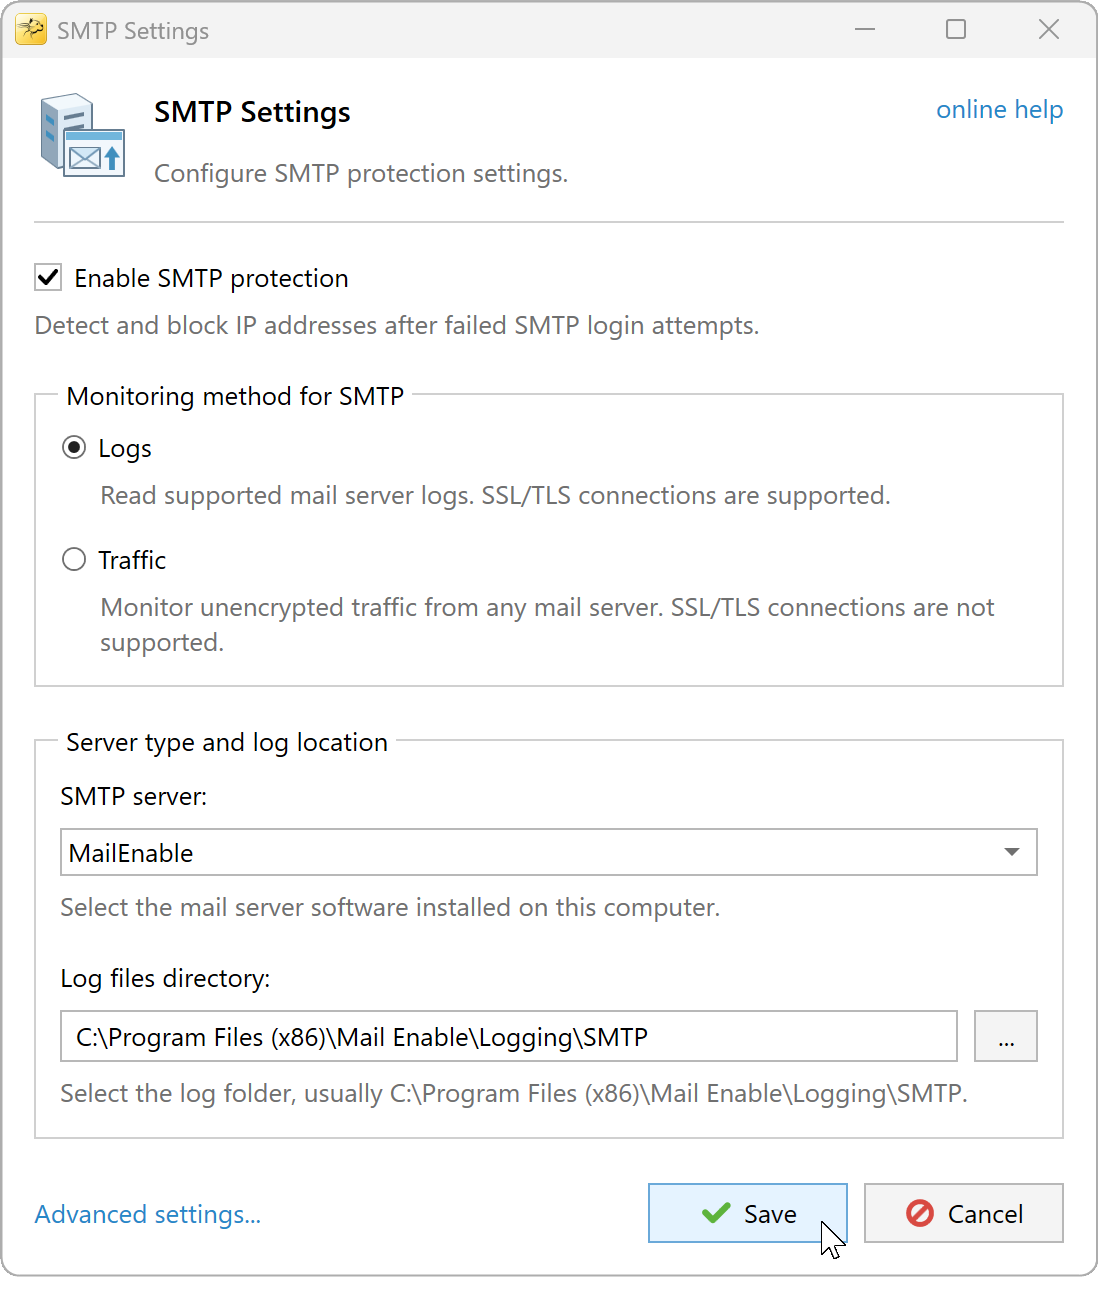
SMTP protection using Logs, with a MailEnable log folder.


Monitoring method for SMTP
Choose how RdpGuard detects failed SMTP login attempts:
Log-based monitoring
Logs is the recommended default method. It uses fewer resources than Traffic and works with SSL/TLS connections. RdpGuard can also detect usernames when they are available in the supported log records.
SMTP server
Select the mail server software installed on this computer:
- MailEnable
- Kerio Connect
- hMailServer
- MS Exchange
- IBM Domino (HCL Domino)
- Axigen Mail Server
- MDaemon Email Server
- SmarterMail
- E-MailRelay
Log location
Make sure server logging is enabled, then specify where RdpGuard should read the logs:
- Kerio Connect: select the
security.logfile. - Axigen: select the
security.txtfile. Enable security logging withenableSecurityLog = yesinaxigen.cfg. - IBM Domino: select the
console.logfile. - MailEnable, hMailServer, MDaemon and SmarterMail: select the server's log folder.
- MS Exchange: select the SMTP receive log folder, or leave the path empty to read the Windows Application Event Log (Event ID 1035).
- E-MailRelay: select the log folder, or leave the path empty to read the Windows Application Event Log. Include client IP addresses in the logs using
--log-addressor--log-format=address; see the E-MailRelay logging options.
Click Save to apply the settings.
Advanced SMTP settings
When using Logs, click Advanced settings... to choose additional events that count toward IP blocking: failed web admin or webmail logins, username enumeration, relay attempts, spam, DNS blacklist matches and missing reverse DNS records.

Supported events depend on the mail server and its log format. RdpGuard reads these events from the server's logs; it does not run spam filtering or DNS checks itself. Click OK, then Save in SMTP Settings.
Traffic-based monitoring
Traffic detects failed logins in unencrypted SMTP traffic without reading server logs. It uses more resources than Logs and does not detect usernames. It cannot inspect SSL/TLS traffic, including connections upgraded with STARTTLS. Use Logs for encrypted connections.

Select Traffic, then choose a capture method:
- WinPcap/Npcap (recommended) - install WinPcap or Npcap, then click Configure... to select the network adapter to monitor.
- Raw Sockets - may affect network performance and may not work with some firewalls or Windows editions.
SMTP ports
Leave this field empty to monitor port 25, or enter the ports used by your SMTP server. Separate multiple ports with commas, for example 25, 587. Adding a port does not enable monitoring of encrypted traffic on that port.
Click Save to apply the settings. To check for monitoring errors, open View, Show event log in RdpGuard Dashboard.
RdpGuard protects:
- Remote Desktop
- MS-SQL Server
- FTP Protocol
- HTTP Protocol
- IMAP Protocol
- POP3 Protocol
- SMTP Protocol
- IIS Web Login
- MySQL Server
- ASP.NET Forms
- RD Web Access
- VoIP (SIP Protocol)
- SSH Protocol
- MS VPN (RRAS)
"This sotware is really great. It's a relief. Because my server is constantly under attack. Thanks RdpGuard" - Joaquim De Sousa Marques
"Nice product. I used to implement something similiar in a low-tech and cumbersome manner via a script called TSBlock (not mine). This makes it much easier and is well worth the pricetag for SMB's." - J. Johnson
"Absolutely amazed at your product. We are a church in the North Dallas area, and I discovered this morning multiple failed logon attempts via our Remote Access Server. A friend suggested your product, so I immediately downloaded the trial. It had a list of about five blocked IP addresses in minutes, and that was enough to lead me to push the BUY button. Over the past 10-15 minutes the list is now about thirty with at least a third being international attempts to break into our system. Thanks for a great product. You may have just saved us much grief." - John Hallford
"Love the software. RDP on our Windows servers is just ridiculous. We would block it in the router but we have lots of old-time customers that would have issues." - Scott Hirsch
"Love the software! Makes it easier than tailoring VB Scripts!!" - Nick Brennan
"It's a great product - really stopping those RDP attackers :-)" - Dave, UK
"First of all: Your application is very (!!!) useful and I like it very much securing my 2012 R2 server. RdpGuard is the best solution, I found on the market and after 10 minutes of testing it I ordered the fully-featured version. :-)" - Carsten Baltes