RD Web Access Protection
Enable and configure RD Web Access protection
RdpGuard monitors IIS logs and Windows Security events to detect brute-force attempts against Remote Desktop Web Access. Configure log discovery below, then use the advanced settings if RD Web Access is behind a reverse proxy.
Open RdpGuard Dashboard and click RD-WEB under Monitored protocols.
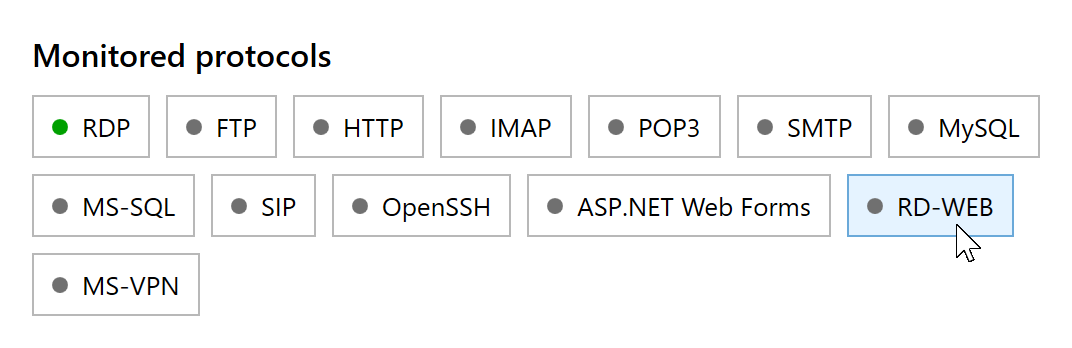
Click RD-WEB to open its protection settings. Select Enable RD Web protection. Leave automatic log discovery enabled or specify the log folder as described below, then click Save.
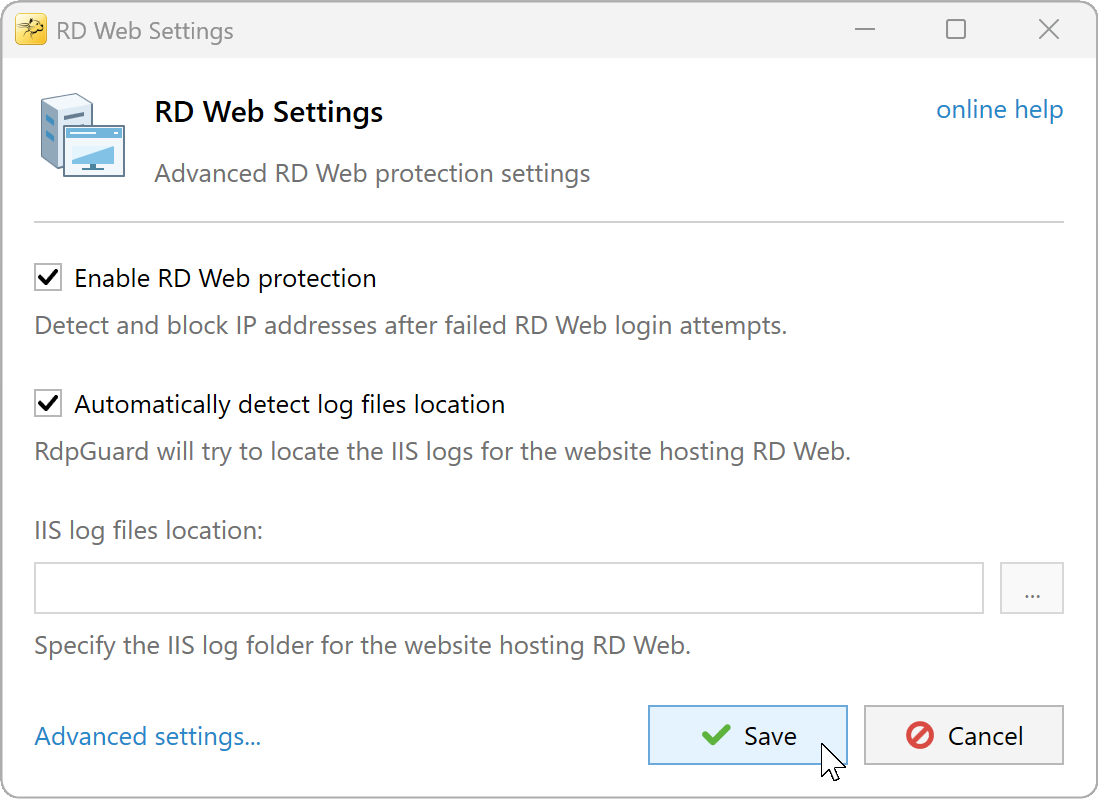
Enable protection and choose how to locate the IIS logs.


RD Web Access protection configuration
Automatically detect log files location lets RdpGuard find the IIS website with the /RDWeb application and use that site's log folder. If discovery fails or you need a different folder, clear this checkbox and specify IIS log files location manually.
Select the folder containing the site's u_ex*.log files, for example C:\inetpub\logs\LogFiles\W3SVC1. The number after W3SVC is the IIS site ID; use the folder for the website hosting RD Web Access.
Enable W3C logging for the site and include these fields: Date (date), Time (time), Client IP Address (c-ip), Method (cs-method), URI Stem (cs-uri-stem) and User Name (cs-username).
For correlation with Windows Security events, enable failed logon auditing as described in Recommended Audit Policy Settings. After saving, check View, Show event log in RdpGuard Dashboard for monitoring errors.
Advanced settings
Click Advanced settings... in RD Web Settings to open Advanced HTTP Settings. These options control how RdpGuard reads client IP addresses from IIS logs.

Read the client IP address from the X-Forwarded-For field
By default, RdpGuard uses Client IP Address (c-ip) from the IIS log. Behind a reverse proxy, this is usually the proxy's address. Enable this option to use the logged X-Forwarded-For value instead. If it contains several addresses, RdpGuard uses the first one.
Configure your trusted proxy to supply the real client IP and prevent clients from injecting their own first address into the header. Restrict direct access to IIS so requests cannot bypass the proxy. See Configuring IIS to Detect Client IP Behind a Proxy for the IIS logging setup.
Use the connection IP address if X-Forwarded-For is missing
Enable this option to use c-ip when the X-Forwarded-For value is missing. Leave it off if every request comes through a proxy: falling back to the connection address can cause the proxy itself to be blocked.
Click OK, then Save in RD Web Settings to apply the changes.
Blocking requests when using X-Forwarded-For
Reading X-Forwarded-For identifies the client, but does not change where blocking happens. When the connection to your server comes from a reverse proxy, a Windows firewall rule for the original client IP will not block that proxied connection.
Block the client at the proxy, or use IIS IP Address and Domain Restrictions with Proxy Mode and RdpGuard Custom Actions as shown below.
Configuring Custom Actions in RdpGuard
This example adds and removes IPv4 deny entries for one IIS website. Replace RD Web Site in both commands with the site's name in IIS Manager.
- Install the IIS IP and Domain Restrictions role service if it is not installed.
- In IIS Manager, select the website, open IP Address and Domain Restrictions, click Edit Feature Settings... and select Enable Proxy Mode. This requires IIS 8.0 or later. See Microsoft's IP Security documentation.
- Run RdpGuard Dashboard as administrator and open Tools, Custom Actions / Notifications. Add the two actions below.
IP Blocked action
- Event: IP Blocked
- Task: Execute program
- Path:
C:\Windows\System32\inetsrv\appcmd.exe
Arguments:
set config "RD Web Site" /section:system.webServer/security/ipSecurity /+"[ipAddress='%IP%',allowed='false']" /commit:apphostIP Unblocked action
- Event: IP Unblocked
- Task: Execute program
- Path:
C:\Windows\System32\inetsrv\appcmd.exe
Arguments:
set config "RD Web Site" /section:system.webServer/security/ipSecurity /-"[ipAddress='%IP%']" /commit:apphostSave the actions. After a local detection triggers a block, verify that the deny entry appears for the selected IIS site and requests from that client are denied through the proxy. When RdpGuard unblocks the address, the second action removes the entry.
These actions handle future IP Blocked and IP Unblocked events from local detections; they do not synchronize the existing blocked list or addresses blocked only through IP Cloud.
RdpGuard protects:
- Remote Desktop
- MS-SQL Server
- FTP Protocol
- HTTP Protocol
- IMAP Protocol
- POP3 Protocol
- SMTP Protocol
- IIS Web Login
- MySQL Server
- ASP.NET Forms
- RD Web Access
- VoIP (SIP Protocol)
- SSH Protocol
- MS VPN (RRAS)
"This sotware is really great. It's a relief. Because my server is constantly under attack. Thanks RdpGuard" - Joaquim De Sousa Marques
"Nice product. I used to implement something similiar in a low-tech and cumbersome manner via a script called TSBlock (not mine). This makes it much easier and is well worth the pricetag for SMB's." - J. Johnson
"Absolutely amazed at your product. We are a church in the North Dallas area, and I discovered this morning multiple failed logon attempts via our Remote Access Server. A friend suggested your product, so I immediately downloaded the trial. It had a list of about five blocked IP addresses in minutes, and that was enough to lead me to push the BUY button. Over the past 10-15 minutes the list is now about thirty with at least a third being international attempts to break into our system. Thanks for a great product. You may have just saved us much grief." - John Hallford
"Love the software. RDP on our Windows servers is just ridiculous. We would block it in the router but we have lots of old-time customers that would have issues." - Scott Hirsch
"Love the software! Makes it easier than tailoring VB Scripts!!" - Nick Brennan
"It's a great product - really stopping those RDP attackers :-)" - Dave, UK
"First of all: Your application is very (!!!) useful and I like it very much securing my 2012 R2 server. RdpGuard is the best solution, I found on the market and after 10 minutes of testing it I ordered the fully-featured version. :-)" - Carsten Baltes