RDP Exclusions for Security Event ID 4625
Security Log Event ID 4625 overview
RdpGuard uses Windows Security event 4625 to detect failed login attempts. These events can come from Remote Desktop connections, network shares, services or scheduled tasks. Attempts detected by this engine appear as RDP in the Dashboard, even when they originate from another type of Windows logon.
Use exclusion rules when you can identify legitimate activity by specific event fields. Matching events are skipped by the RDP detection engine. To exempt a trusted IP address from blocking altogether, use the whitelist.
In Event Viewer, Windows Logs, Security, open an event with Event ID 4625:

How to configure RDP exclusions
Open RdpGuard Dashboard and click RDP under Monitored protocols.
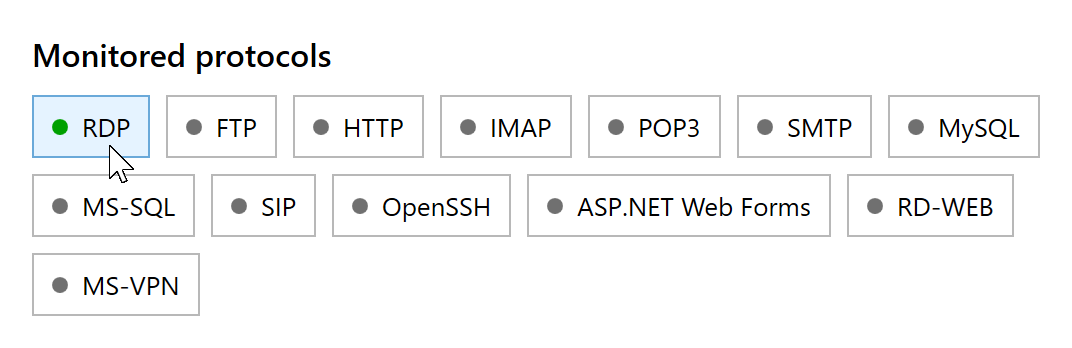
Click RDP to open its protection settings. In RDP Settings, click Exclusions....
Enable RDP protection must be selected to edit exclusions.
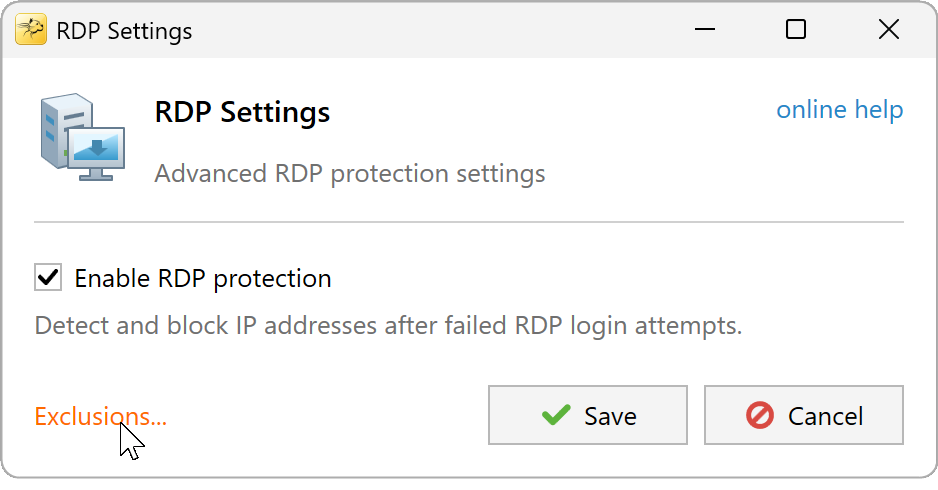
Click Exclusions to edit the rules. Enter one rule per line in RDP Exclusions, then click OK.
The syntax and examples below explain how to write rules.
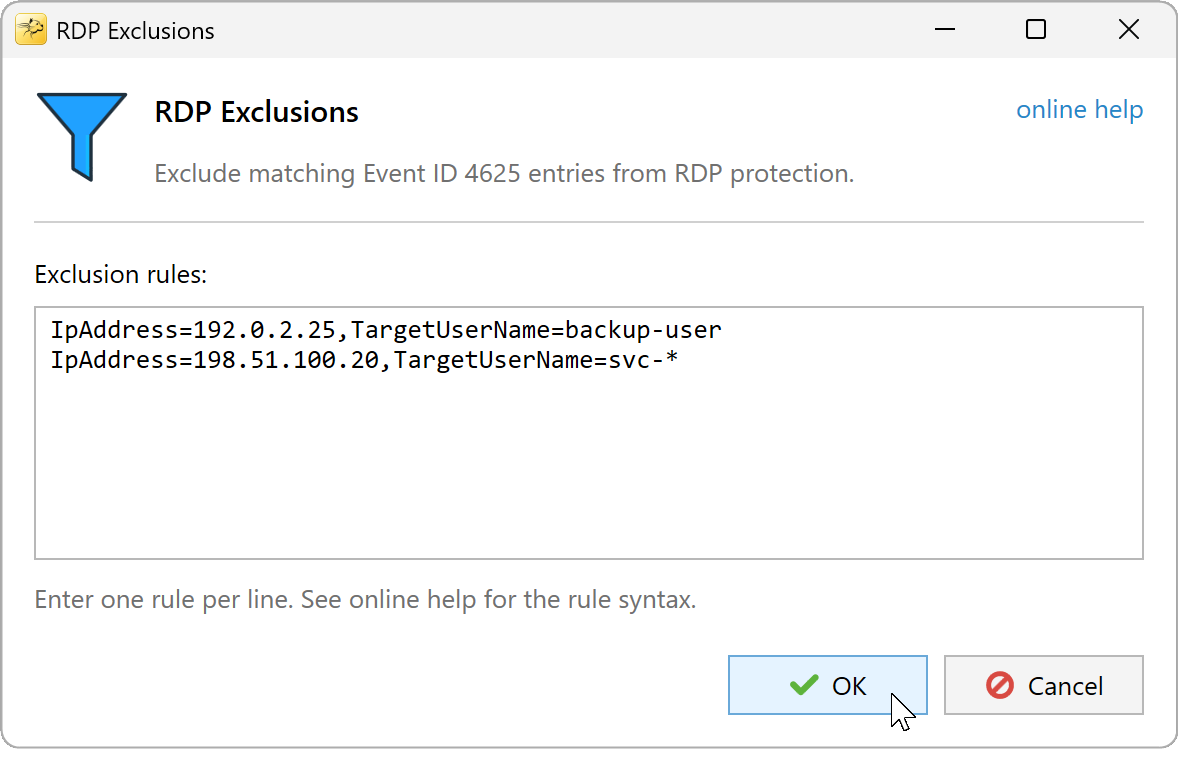
Enter exclusion rules and click OK. Click Save in RDP Settings to apply the exclusions.


Exclusion rules syntax and examples
Write each rule on a separate line. Separate conditions within a rule with commas. An event is excluded if all conditions in any one rule match.
IpAddress=192.0.2.25,TargetUserName=backup-user
IpAddress=198.51.100.20,TargetUserName=svc-*
The first rule excludes events for backup-user from 192.0.2.25. The second excludes events for usernames beginning with svc- from 198.51.100.20. Replace these example addresses and usernames with values from the events you want to exclude.
Matching rules
=matches a value or wildcard pattern;!=matches values that do not match it.*matches any sequence of characters;?matches one character.- Conditions separated by commas use AND. Rules on separate lines use OR.
- Field names and values are case-sensitive. Copy their spelling and case from the event XML.
- If a field is absent from the event, a condition using it does not match, including a
!=condition. - Lines beginning with
#are comments.
For example, IpAddress=192.0.2.25,TargetUserName!=backup-user matches other usernames from that address. Keep conditions on the same line when they must match together. Putting an IP address and a username on separate lines creates two independent exclusions.
Fields available for RDP exclusions
Open the event's Details tab and select XML View. Use the names and values inside EventData. For example, <Data Name="LogonType">3</Data> provides the field LogonType with value 3.
Example XML for the event shown above:
<Event xmlns="http://schemas.microsoft.com/win/2004/08/events/event">
  <System>
    <Provider Name="Microsoft-Windows-Security-Auditing"
      Guid="{54849625-5478-4994-a5ba-3e3b0328c30d}" />
    <EventID>4625</EventID>
    <Version>0</Version>
    <Level>0</Level>
    <Task>12544</Task>
    <Opcode>0</Opcode>
    <Keywords>0x8010000000000000</Keywords>
    <TimeCreated SystemTime="2026-09-29T08:06:12.6465802Z" />
    <EventRecordID>27682099</EventRecordID>
    <Correlation
      ActivityID="{96b13ecf-444f-0004-fa3e-b1964f44dd01}" />
    <Execution ProcessID="764" ThreadID="140" />
    <Channel>Security</Channel>
    <Computer>SERVER01</Computer>
    <Security />
  </System>
  <EventData>
    <Data Name="SubjectUserSid">S-1-0-0</Data>
    <Data Name="SubjectUserName">-</Data>
    <Data Name="SubjectDomainName">-</Data>
    <Data Name="SubjectLogonId">0x0</Data>
    <Data Name="TargetUserSid">S-1-0-0</Data>
    <Data Name="TargetUserName">Admin</Data>
    <Data Name="TargetDomainName">.</Data>
    <Data Name="Status">0xc000006d</Data>
    <Data Name="FailureReason">%%2313</Data>
    <Data Name="SubStatus">0xc0000064</Data>
    <Data Name="LogonType">3</Data>
    <Data Name="LogonProcessName">NtLmSsp</Data>
    <Data Name="AuthenticationPackageName">NTLM</Data>
    <Data Name="WorkstationName">-</Data>
    <Data Name="TransmittedServices">-</Data>
    <Data Name="LmPackageName">-</Data>
    <Data Name="KeyLength">0</Data>
    <Data Name="ProcessId">0x0</Data>
    <Data Name="ProcessName">-</Data>
    <Data Name="IpAddress">95.47.156.55</Data>
    <Data Name="IpPort">0</Data>
  </EventData>
</Event>| Field | Description |
|---|---|
TargetUserName | Account name used in the failed logon. |
TargetDomainName | Domain or computer name of that account. |
TargetUserSid | Security identifier of that account. |
IpAddress | Source IP address recorded in the event. |
IpPort | Source port recorded in the event. |
LogonType | Numeric logon type, such as 3 for a network logon. |
WorkstationName | Name of the source computer. |
ProcessName | Full path of the process that attempted the logon. |
ProcessId | ID of that process. |
Status | Logon failure status code. |
SubStatus | Additional failure status code. |
FailureReason | Failure reason value as stored in XML. |
SubjectUserSid | SID of the account that reported the failure. |
SubjectUserName | Name of the account that reported the failure. |
SubjectDomainName | Domain or computer name of that account. |
SubjectLogonId | Logon ID of the reporting account. |
LogonProcessName | Name of the trusted logon process. |
AuthenticationPackageName | Authentication package, such as NTLM or Kerberos. |
TransmittedServices | Services involved in Kerberos delegation. |
LmPackageName | NTLM subpackage name, when applicable. |
KeyLength | NTLM session key length, when applicable. |
Not every field has a useful value in every event. Use the value actually recorded in XML; for example, FailureReason may contain a code such as %%2313, rather than the description shown on the General tab. For full field definitions, see Microsoft's Event 4625 reference.
Using this syntax for other exclusions
The same rule syntax is used for successful logon exclusions in Custom Actions and successful logon logging. The available fields depend on the event and where the rule is applied.
For successful logon notifications, RdpGuard supplies Protocol, TargetUserName and IpAddress. Windows logon events can also supply their original EventData fields. For example, Protocol=FTP,TargetUserName=backup-user excludes successful FTP logon notifications for that account.
Protocol is added by RdpGuard; it is not an EventData field in event 4625 and is not available in the RDP Exclusions dialog.
RdpGuard protects:
- Remote Desktop
- MS-SQL Server
- FTP Protocol
- HTTP Protocol
- IMAP Protocol
- POP3 Protocol
- SMTP Protocol
- IIS Web Login
- MySQL Server
- ASP.NET Forms
- RD Web Access
- VoIP (SIP Protocol)
- SSH Protocol
- MS VPN (RRAS)
"This sotware is really great. It's a relief. Because my server is constantly under attack. Thanks RdpGuard" - Joaquim De Sousa Marques
"Nice product. I used to implement something similiar in a low-tech and cumbersome manner via a script called TSBlock (not mine). This makes it much easier and is well worth the pricetag for SMB's." - J. Johnson
"Absolutely amazed at your product. We are a church in the North Dallas area, and I discovered this morning multiple failed logon attempts via our Remote Access Server. A friend suggested your product, so I immediately downloaded the trial. It had a list of about five blocked IP addresses in minutes, and that was enough to lead me to push the BUY button. Over the past 10-15 minutes the list is now about thirty with at least a third being international attempts to break into our system. Thanks for a great product. You may have just saved us much grief." - John Hallford
"Love the software. RDP on our Windows servers is just ridiculous. We would block it in the router but we have lots of old-time customers that would have issues." - Scott Hirsch
"Love the software! Makes it easier than tailoring VB Scripts!!" - Nick Brennan
"It's a great product - really stopping those RDP attackers :-)" - Dave, UK
"First of all: Your application is very (!!!) useful and I like it very much securing my 2012 R2 server. RdpGuard is the best solution, I found on the market and after 10 minutes of testing it I ordered the fully-featured version. :-)" - Carsten Baltes